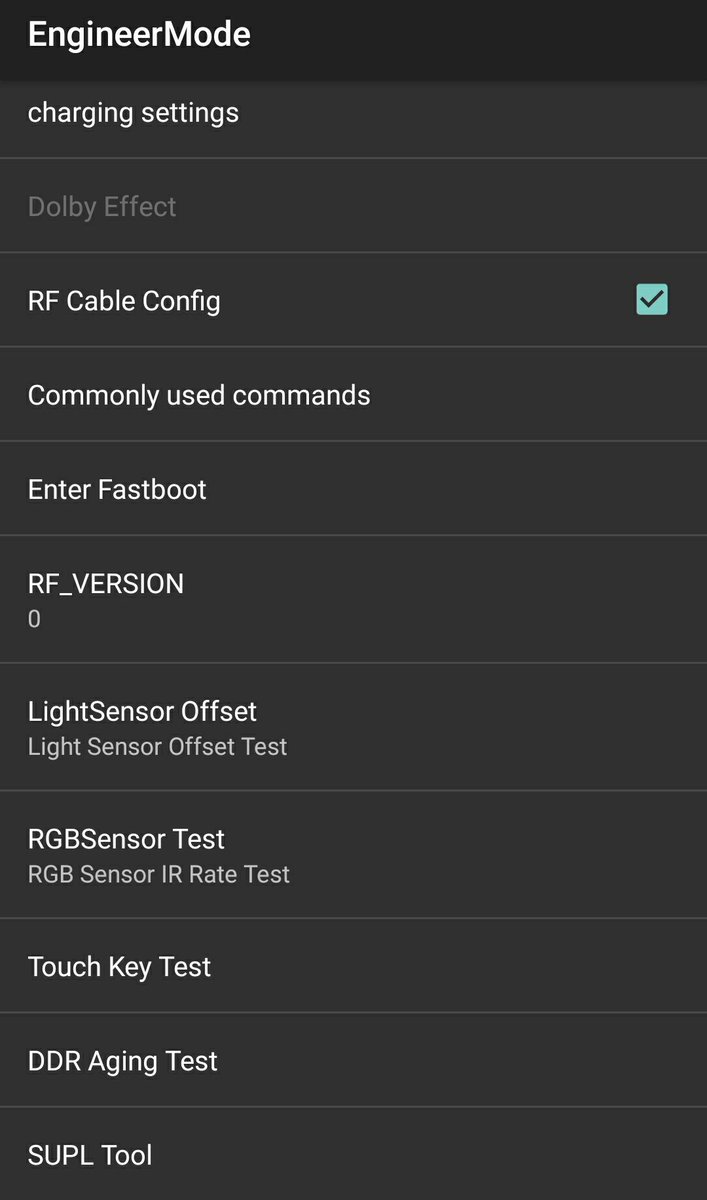
<Thread> Hey @OnePlus! I don't think this EngineerMode APK must be in an user build...🤦♂️
This app is a system app made by @Qualcomm and customised by @OnePlus. It's used by the operator in the factory to test the devices.
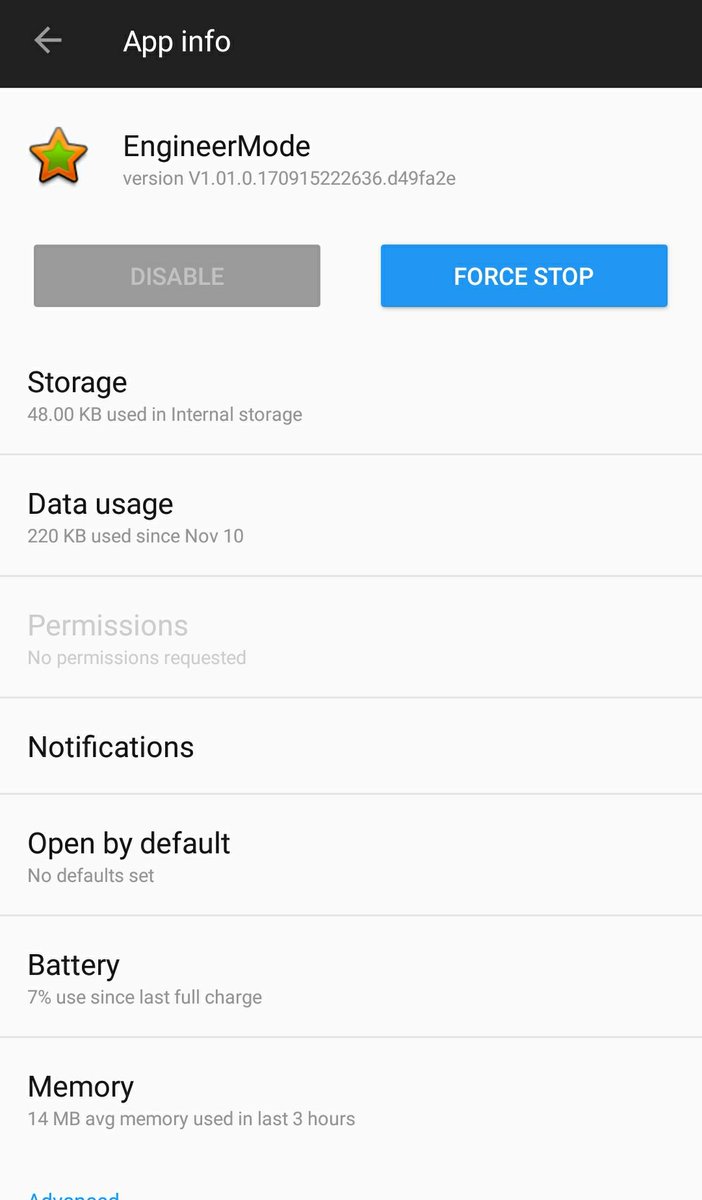
If you have an OnePlus device, I'm pretty sure you have this app pre-installed. To check open Settings -> Apps -> Menu -> Show system apps and search EngineerMode in the app list to check
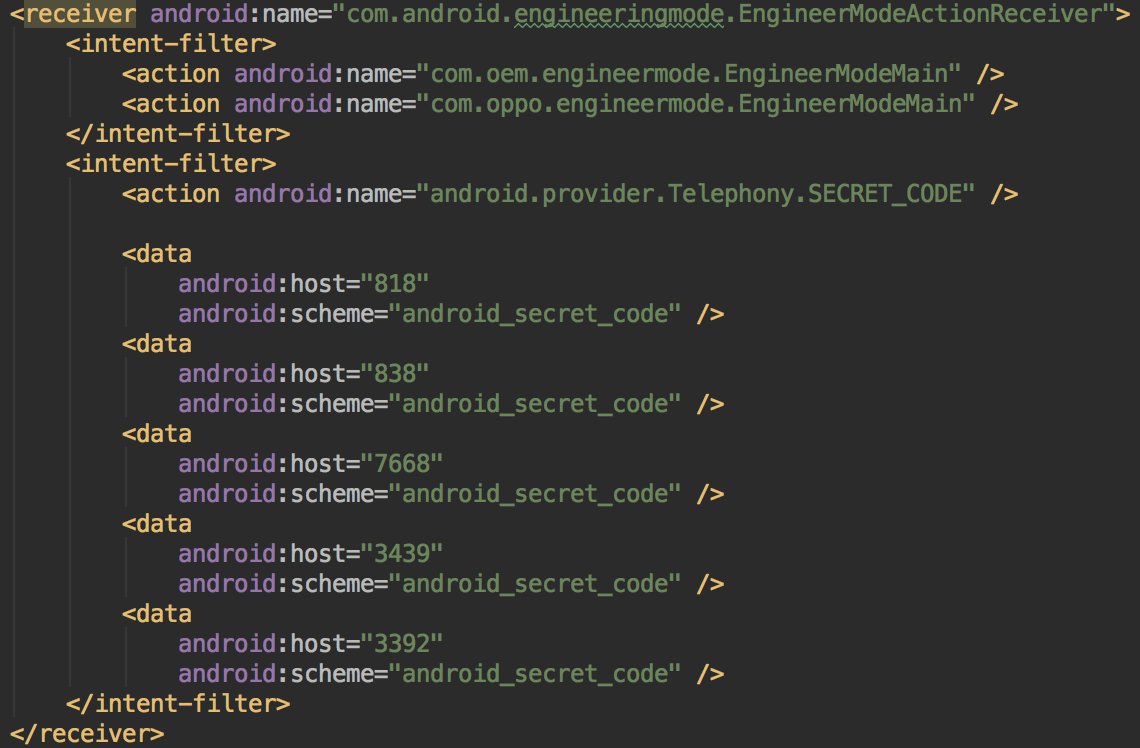
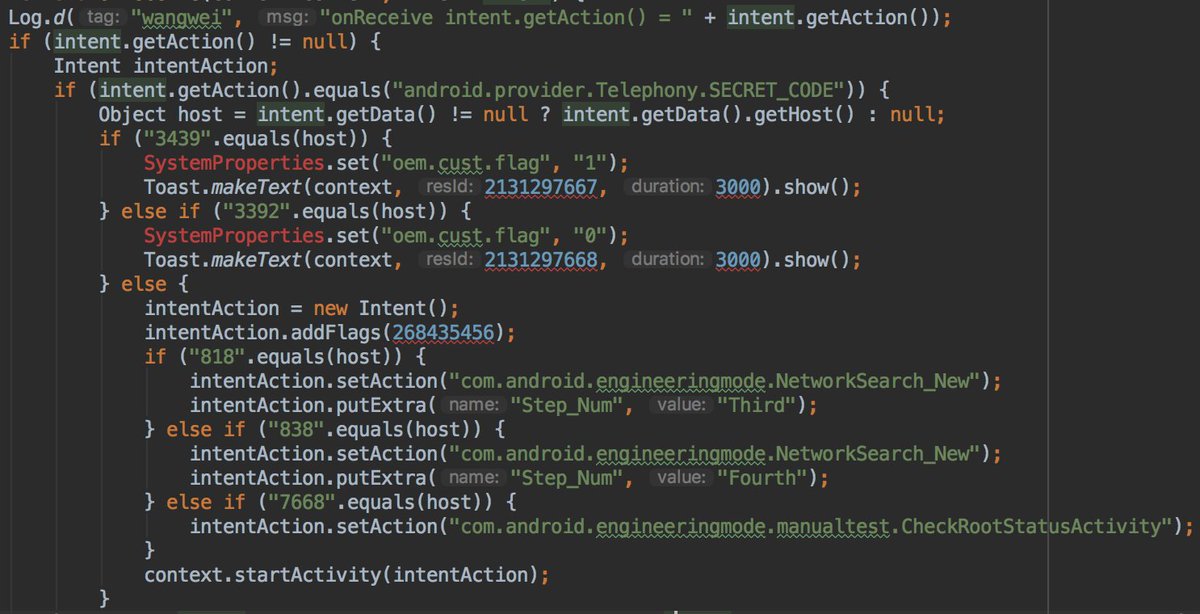
With telephony secret code you can access to manual tests like GPS test, root status test as stated in this article pointed by @AleGrechi . But can do better...
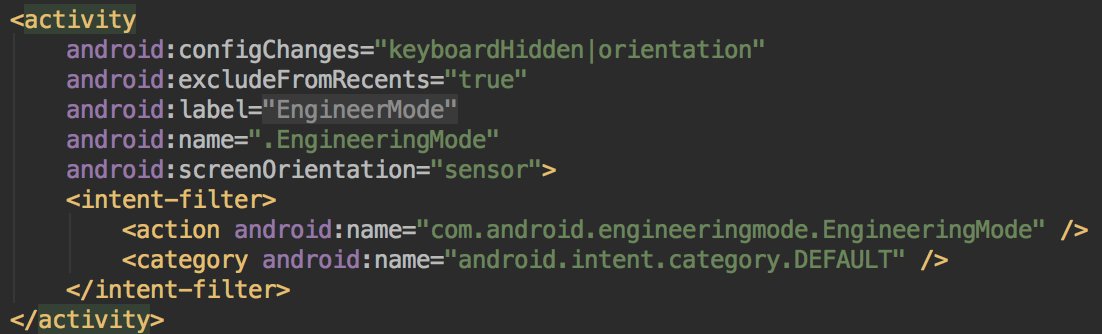
You can access to the "main" activity by sending this command: adb shell am start .engineeringmode/.EngineeringMode
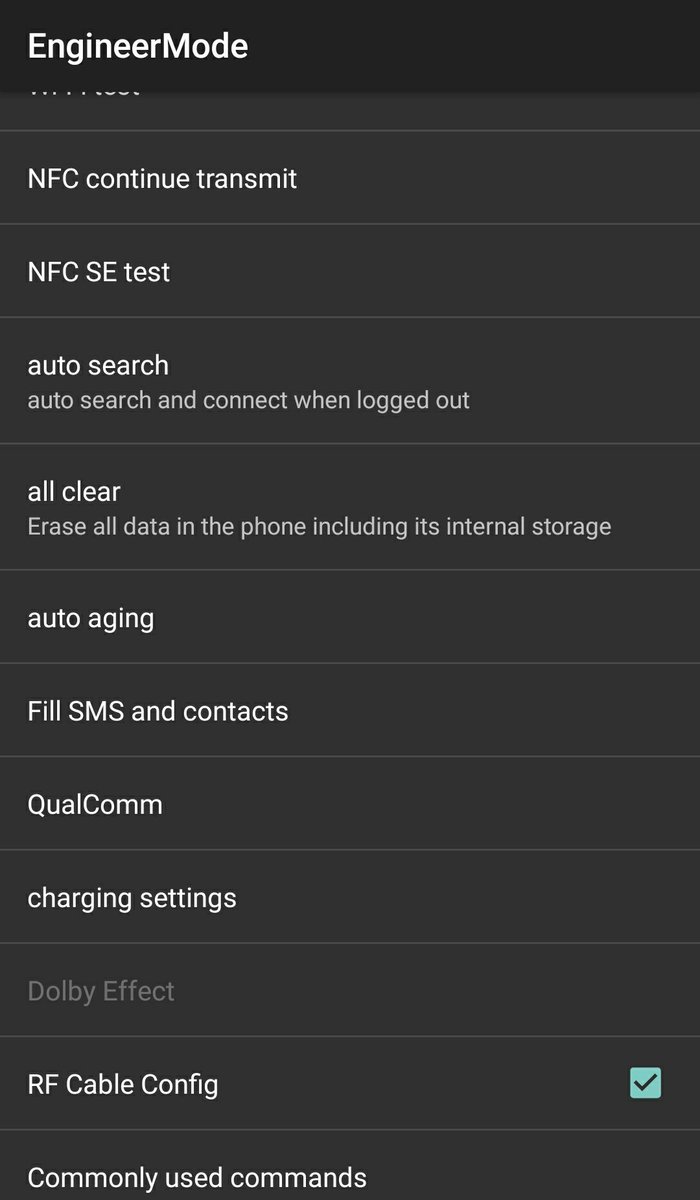
You will have access to everything, not just the manual test.
I will find time to make a POC.
But it's not the biggest issue with this app.
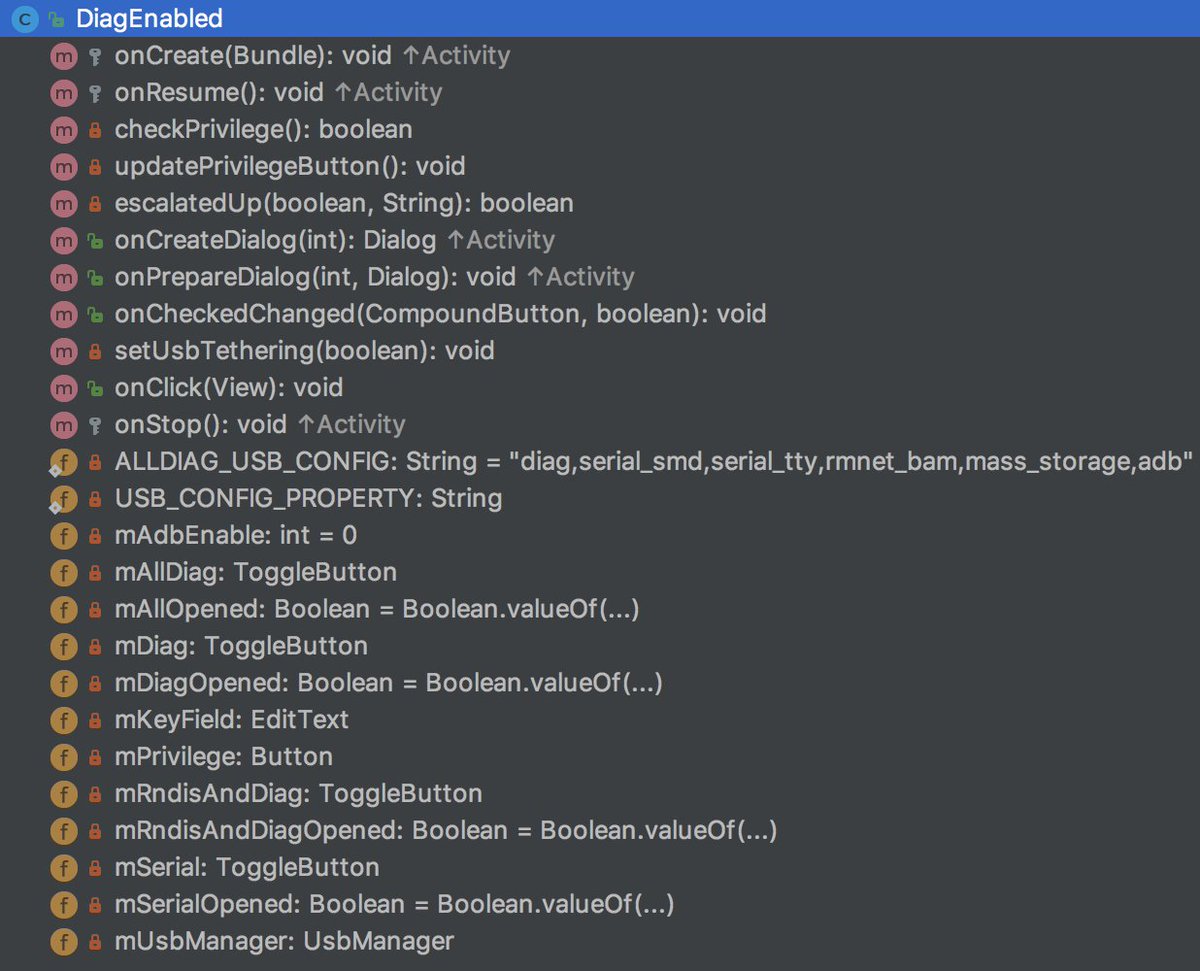
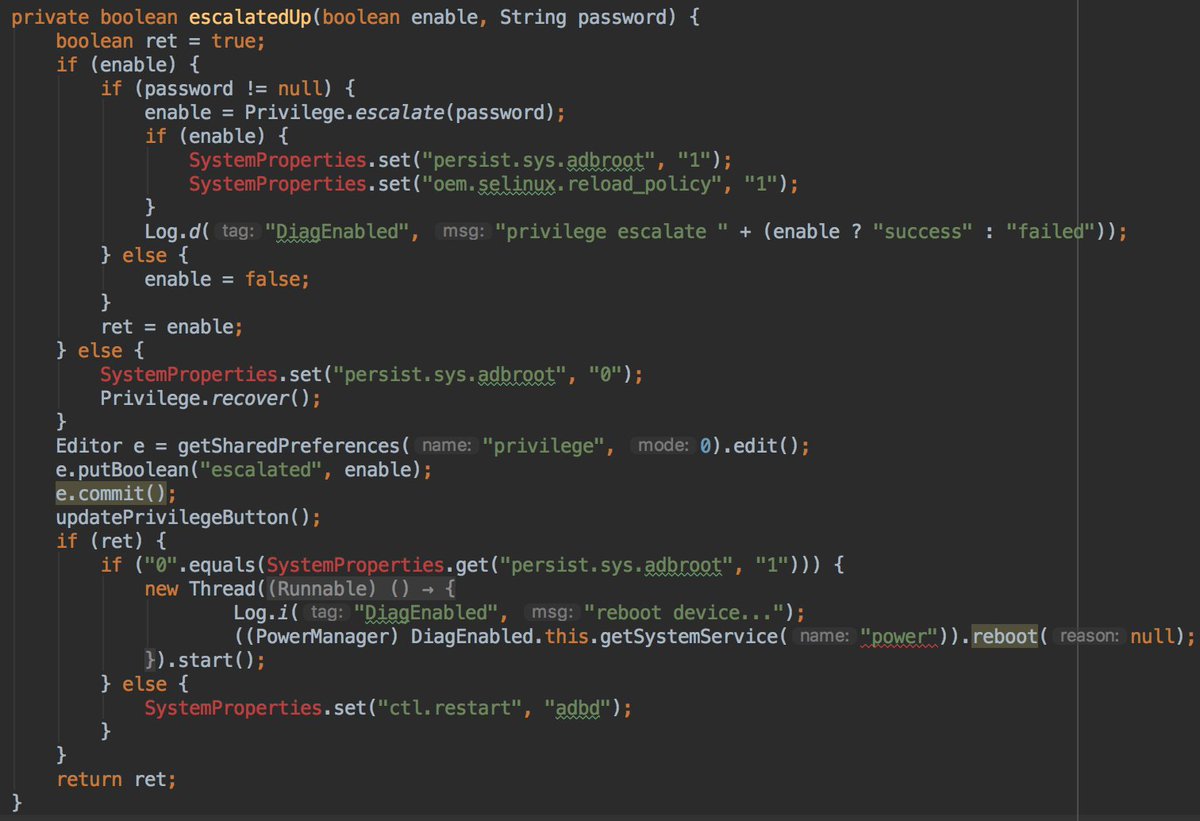
The DiagEnabled, which is a @Qualcomm made activity, is the best class in this EngineerMode APK. Check the methods in this activity: escalatedUp(boolean, string) sounds like a cool thing no 😀?
In the onCreate method if the intent is not null the escalatedUp method is called with the parameter enable=true and password=getIntent().getStringExtra("code"). Do you see where I'm going?
The escalatedUp method is calling Privilege.escalate(password) and if the result is true, it set the system property persist.sys.adbroot and oem.selinux.reload_policy to 1
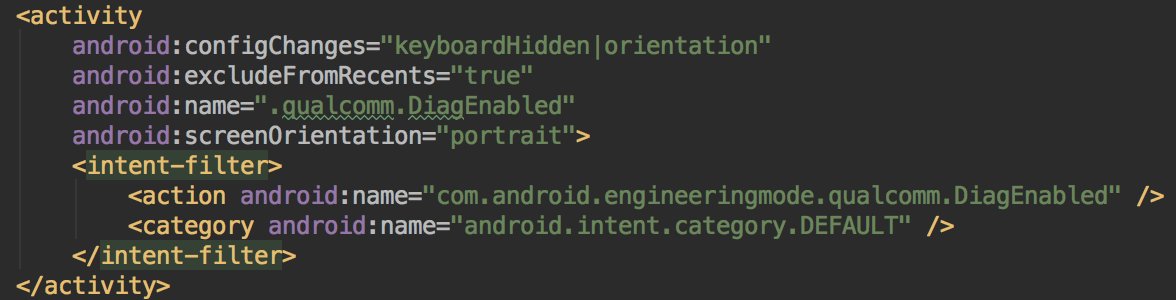
So yes, if you send the command: adb shell am start -n .engineeringmode/.qualcomm.DiagEnabled --es "code" "password" with the correct code you can become root!
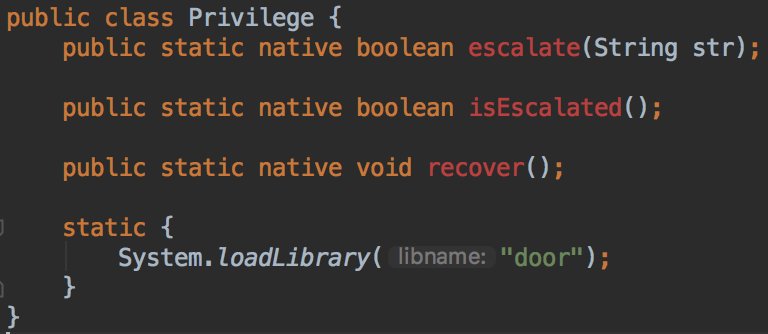
Here the Privilege class. Check the name of native library used to check the code: door... Ladies and Gentlemen please say hi to the backdoor made in @Qualcomm
This lib is located in /system/lib/libdoor.so or /system/lib64/libdoor.so. You can find the sample here:
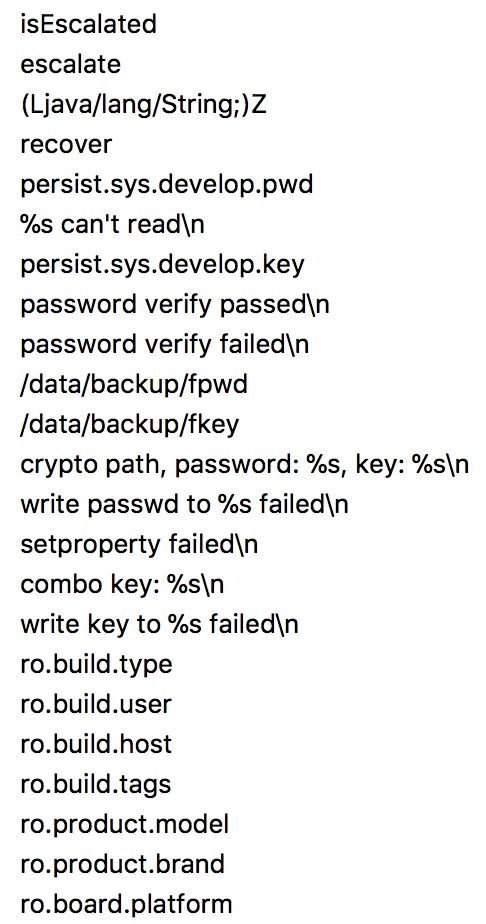
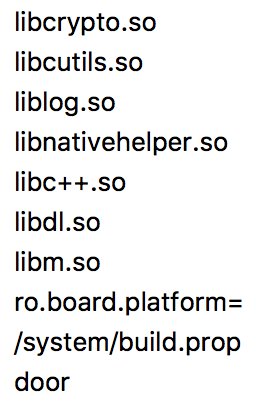
This is the interesting strings of the lib. After a first read we can see that libcrypto is used and the key and the password are backup in /data/backup/fpwd and /data/backup/fkey
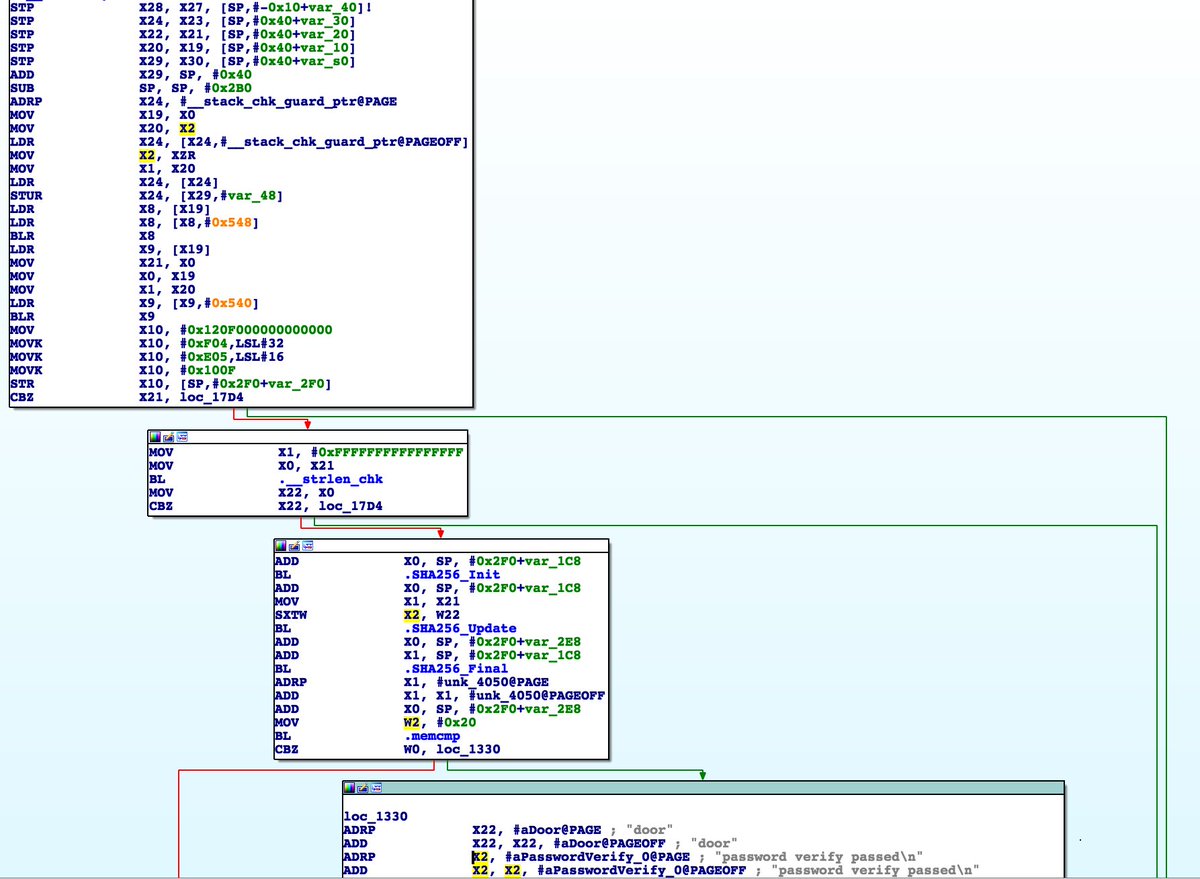
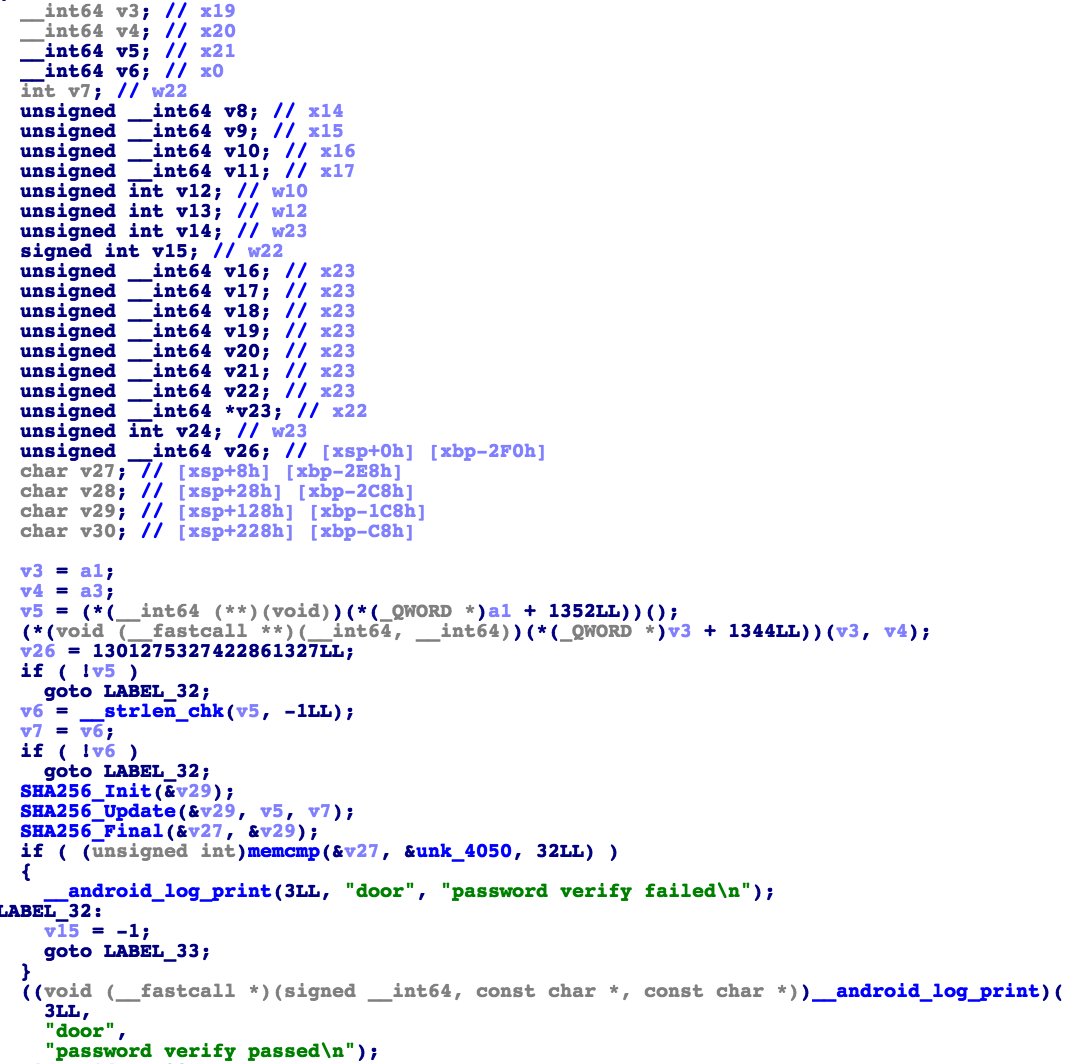
This is the code responsible of the password verification. 1st it check the length, calculate the hash and compare it to the correct one.
Unfortunately, I didn't find the password, so if some you are skilled in reversing native lib, your help is very welcome!
cc @JAMESWT_MHT I forgot to add you :)
<Thread> Hey @OnePlus! I don't think this EngineerMode APK must be in an user build...🤦♂️
This app is a system app made by @Qualcomm and customised by @OnePlus. It's used by the operator in the factory to test the devices.If you have an OnePlus device, I'm pretty sure you have this app pre-installed. To check open Settings -> Apps -> Menu -> Show system apps and search EngineerMode in the app list to checkWith telephony secret code you can access to manual tests like GPS test, root status test as stated in this article pointed by @AleGrechi . But can do better...You can access to the "main" activity by sending this command: adb shell am start .engineeringmode/.EngineeringMode
You will have access to everything, not just the manual test.Having access to all these functions is a real issue. Combined with this attack, , a malicious app can do a lot of thing.I will find time to make a POC.
But it's not the biggest issue with this app.The DiagEnabled, which is a @Qualcomm made activity, is the best class in this EngineerMode APK. Check the methods in this activity: escalatedUp(boolean, string) sounds like a cool thing no 😀?In the onCreate method if the intent is not null the escalatedUp method is called with the parameter enable=true and password=getIntent().getStringExtra("code"). Do you see where I'm going?The escalatedUp method is calling Privilege.escalate(password) and if the result is true, it set the system property persist.sys.adbroot and oem.selinux.reload_policy to 1So yes, if you send the command: adb shell am start -n .engineeringmode/.qualcomm.DiagEnabled --es "code" "password" with the correct code you can become root!Here the Privilege class. Check the name of native library used to check the code: door... Ladies and Gentlemen please say hi to the backdoor made in @QualcommThis lib is located in /system/lib/libdoor.so or /system/lib64/libdoor.so. You can find the sample here:This is the interesting strings of the lib. After a first read we can see that libcrypto is used and the key and the password are backup in /data/backup/fpwd and /data/backup/fkeyThis is the code responsible of the password verification. 1st it check the length, calculate the hash and compare it to the correct one.Unfortunately, I didn't find the password, so if some you are skilled in reversing native lib, your help is very welcome!cc @JAMESWT_MHT I forgot to add you :)
yes
<Thread> Hey @OnePlus! I don't think this EngineerMode APK must be in an user build...🤦️
This app is a system app made by @Qualcomm and customised by @OnePlus. It's used by the operator in the factory to test the devices. ... If you have an OnePlus device, I'm pretty sure you have this app pre-installed. To check open Settings -> Apps -> Menu -> Show system apps and search EngineerMode in the app list to check ... With telephony secret code you can access to manual tests like GPS test, root status test as stated in this article pointed by @AleGrechi . But can do better... ... You can access to the "main" activity by sending this command: adb shell am start .engineeringmode/.EngineeringMode
You will have access to everything, not just the manual test. ... Having access to all these functions is a real issue. Combined with this attack, , a malicious app can do a lot of thing. ... I will find time to make a POC.
But it's not the biggest issue with this app. ... The DiagEnabled, which is a @Qualcomm made activity, is the best class in this EngineerMode APK. Check the methods in this activity: escalatedUp(boolean, string) sounds like a cool thing no ? ... In the onCreate method if the intent is not null the escalatedUp method is called with the parameter enable=true and password=getIntent().getStringExtra("code"). Do you see where I'm going? ... The escalatedUp method is calling Privilege.escalate(password) and if the result is true, it set the system property persist.sys.adbroot and oem.selinux.reload_policy to 1 ... So yes, if you send the command: adb shell am start -n .engineeringmode/.qualcomm.DiagEnabled --es "code" "password" with the correct code you can become root! ... Here the Privilege class. Check the name of native library used to check the code: door... Ladies and Gentlemen please say hi to the backdoor made in @Qualcomm ... This lib is located in /system/lib/libdoor.so or /system/lib64/libdoor.so. You can find the sample here: ... This is the interesting strings of the lib. After a first read we can see that libcrypto is used and the key and the password are backup in /data/backup/fpwd and /data/backup/fkey ... This is the code responsible of the password verification. 1st it check the length, calculate the hash and compare it to the correct one. ... Unfortunately, I didn't find the password, so if some you are skilled in reversing native lib, your help is very welcome! ... cc @JAMESWT_MHT I forgot to add you :)
Missing some Tweet in this thread? You can try to
Update